

ServiceNow
Sr. Manager, Customer Success – Healthcare Cybersecurity ( Armis/ Veza)
It all started when engineer Fred Luddy wrote code that automated a tedious task for his coworker, Phyllis. She cried tears of joy. That moment inspired Fred to build a company that could do that for everyone—freeing people from busywork so they could focus on meaningful work. Today, ServiceNow is the AI control tower for business reinvention. Our ServiceNow AI platform brings together any AI, any data, and any workflow— helping 85% of the Fortune 500® work smarter, faster, and better. We're building an AI-native culture where technology and talent are unstoppable together. And we're just getting started.
Join us to put AI to work for people.
Job Description
Sr. Manager, Customer Success – Healthcare Cybersecurity
About the Role
The Sr. Manager of Customer Success leads Armis's healthcare customer success portfolio, serving as the strategic bridge between technical teams and healthcare stakeholders (clinical IT, biomedical engineering, compliance, security operations). You'll own portfolio performance across hospital systems and healthcare enterprises, mentor Technical CSMs supporting complex medical device and clinical network environments, and ensure consistent execution of strategies that drive adoption of OT/IT security across hospitals, labs, imaging centers, and clinical workflows. You'll translate healthcare compliance and operational realities into scalable success frameworks.
Key Responsibilities
- Own regional ARR planning and attainment for healthcare accounts. Align resources to customer segmentation maturity levels, clinical network complexity, and regulatory timelines; run cadence reviews and intervene early on retention risks tied to medical device visibility or compliance gaps.
- Standardize healthcare-specific EBR narratives around clinical network security outcomes (segmentation velocity, device inventory completeness, incident response readiness) and risk metrics. Partner with customers on FDA cybersecurity compliance storytelling and HIPAA/HITECH audit readiness.
- Establish and enforce portfolio-level healthcare risk playbooks. Chair recurring risk reviews focused on critical device vulnerabilities, unmanaged endpoint exposure, and segmentation gaps; coordinate cross-functional mitigations with biomedical, IT, and security teams.
- Operationalize healthcare network design reviews and security standards across the portfolio. Define best practices for DICOM/HL7 protocol visibility, clinical VLAN segmentation, NAC enforcement, and medical device inventory governance. Scale reusable patterns that accelerate time-to-value for multi-site hospital systems.
- Run regional Voice of Customer cadences focused on healthcare-specific use cases. Aggregate clinical IT and biomedical requests into prioritized asks (e.g., remote maintenance security, OT/IT convergence visibility, wireless medical device monitoring); coordinate beta engagements and close feedback loops with Product and clinical advisory boards.
- Establish enablement agenda for the healthcare team. Build proficiency baselines on medical device types (imaging, monitoring, therapeutic, lab), clinical communication protocols (HL7, DICOM, IEEE 11073, BACnet, Modbus), healthcare compliance frameworks (IEC 80001, NIST CSF for Healthcare, HIPAA Security Rule), and ensure expert coverage for complex architectures and incident response scenarios.
- Own healthcare onboarding standards and playbooks. Define discovery workflows for multi-facility deployments, clinical network assessments, and medical device inventory projects. Measure adoption of best practices across segmentation, patching, and incident coordination.
- Scale healthcare vertical frameworks. Tailor strategies for different customer profiles (academic medical centers vs. community hospitals vs. integrated delivery networks) and regulatory contexts (FDA premarket requirements, state healthcare data breach laws, CMS security standards).
- Drive customer-to-product feedback loops. Maintain relationships with healthcare advisory boards and clinical IT leaders; advocate for product enhancements around medical device discovery, clinical protocol monitoring, and healthcare-specific compliance reporting.
- Model ethical decision-making on healthcare security trade-offs (balancing security hardening against clinical operational continuity). Hold team accountable to balanced customer outcomes and organizational targets.
- Cultivate a learning culture. Run retros on customer implementations, institutionalize playbooks for common healthcare scenarios (device compromise, network anomalies, remote access hardening), and build skills roadmaps for Technical CSMs working in healthcare environments.
Qualifications
- 10+ years in Customer Success, Account Management, Solutions Engineering, or Consulting within B2B SaaS or enterprise cybersecurity, with 5+ years focused on healthcare IT, medical device security, or clinical network environments.
- Proven track record managing technical portfolios and leading teams in healthcare cybersecurity, OT/IT convergence, or medical device security.
- Deep understanding of healthcare network infrastructure (clinical VLANs, medical device protocols, segmentation, remote access for biomedical vendors).
- Demonstrated fluency with healthcare communication protocols (DICOM, HL7/FHIR, IEEE 11073, BACnet, Modbus) and ability to translate protocol security implications to clinical stakeholders.
- Strong knowledge of healthcare compliance frameworks (HIPAA, HITECH, FDA cybersecurity premarket/postmarket guidance, IEC 80001, NIST CSF for Healthcare).
- Exceptional ability to manage relationships across technical and clinical stakeholders (biomedical engineers, clinical IT directors, compliance officers, hospital security teams).
- Track record of managing large, complex healthcare customer implementations (multi-site systems, high-touch deployments, regulatory audits).
- Bachelor's degree in IT, Computer Science, Healthcare IT, Biomedical Engineering, or related discipline (required); advanced degree or equivalent healthcare security experience preferred.
Preferred Attributes
- Experience with healthcare-specific cybersecurity or visibility platforms (Claroty, Dragos, Nozomi, or similar OT/medical device security solutions).
- Experience working with biomedical engineering teams or clinical IT leadership on device security and network architecture projects.
- Familiarity with healthcare incident response workflows and coordination across clinical, IT, and security operations teams.
- Knowledge of hospital architecture standards (e.g., AAMI TIR57 guidelines for clinical IT security).
- Strategic systems thinker who excels at translating clinical and compliance complexity into scalable operational frameworks.
- Exceptional communication skills with ability to present security concepts to non-technical clinical leaders and executive stakeholders.
- Data-driven decision-maker with strong portfolio analytics and KPI design experience.
- Empathetic leader committed to developing Technical CSMs and building team capability in healthcare-specific domains.
For positions in this location, we offer a base pay of $158,000 - $208,750, plus equity (when applicable), variable/incentive compensation and benefits. Sales positions generally offer a competitive On Target Earnings (OTE) incentive compensation structure. Please note that the base pay shown is a guideline, and individual total compensation will vary based on factors such as qualifications, skill level, competencies, and work location. We also offer health plans, including flexible spending accounts, a 401(k) Plan with company match, ESPP, matching donations, a flexible time away plan and family leave programs. Compensation is based on the geographic location in which the role is located and is subject to change based on work location.
Additional InformationWork Personas
We approach our distributed world of work with flexibility and trust. Work personas (flexible, remote, or required in office) are categories that are assigned to ServiceNow employees depending on the nature of their work and their assigned work location. Learn more here. To determine eligibility for a work persona, ServiceNow may confirm the distance between your primary residence and the closest ServiceNow office using a third-party service.
Equal Opportunity Employer
ServiceNow is an equal opportunity employer. All qualified applicants will receive consideration for employment without regard to race, color, religion, sex, sexual orientation, national origin, age, disability, gender identity, veteran status, or any other category protected by law. In addition, all qualified applicants with arrest or conviction records will be considered for employment in accordance with legal requirements.
Accommodations
We strive to create an accessible and inclusive experience for all candidates. If you require a reasonable accommodation to complete any part of the application process, or are unable to use this online application and need an alternative method to apply, please contact [email protected] for assistance.
Export Control Regulations
For positions requiring access to controlled technology subject to export control regulations, including the U.S. Export Administration Regulations (EAR), ServiceNow may be required to obtain export control approval from government authorities for certain individuals. All employment is contingent upon ServiceNow obtaining any export license or other approval that may be required by relevant export control authorities.
From Fortune. ©2026 Fortune Media IP Limited. All rights reserved. Used under license.
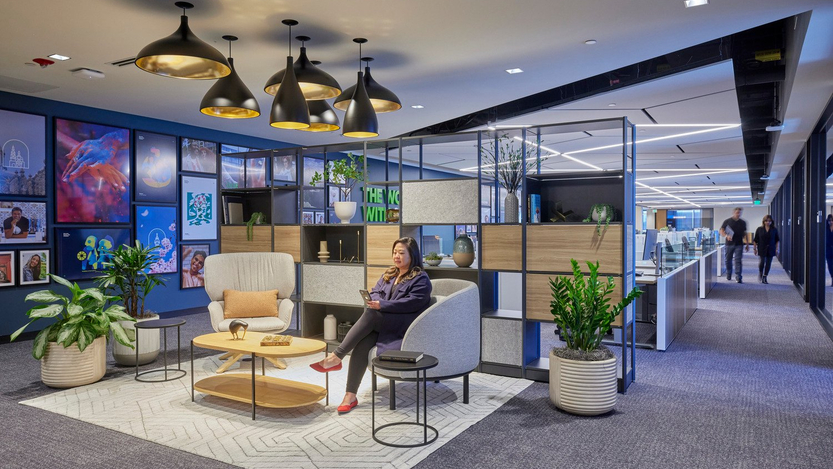
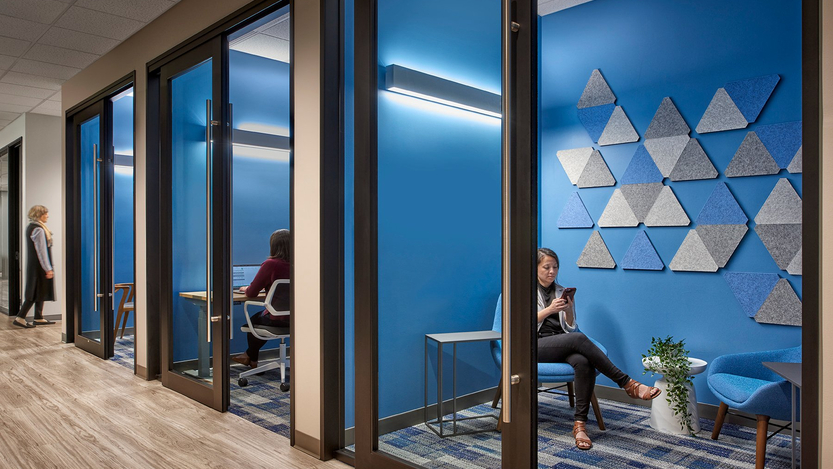
ServiceNow Denver, Colorado, USA Office



1800 Wazee St, Suite 300, Denver, CO, United States, 80202
Similar Jobs at ServiceNow
What you need to know about the Colorado Tech Scene
Key Facts About Colorado Tech
- Number of Tech Workers: 260,000; 8.5% of overall workforce (2024 CompTIA survey)
- Major Tech Employers: Lockheed Martin, Century Link, Comcast, BAE Systems, Level 3
- Key Industries: Software, artificial intelligence, aerospace, e-commerce, fintech, healthtech
- Funding Landscape: $4.9 billion in VC funding in 2024 (Pitchbook)
- Notable Investors: Access Venture Partners, Ridgeline Ventures, Techstars, Blackhorn Ventures
- Research Centers and Universities: Colorado School of Mines, University of Colorado Boulder, University of Denver, Colorado State University, Mesa Laboratory, Space Science Institute, National Center for Atmospheric Research, National Renewable Energy Laboratory, Gottlieb Institute
